Excellent career opportunities with the UK's leading Security Service MI5.
https://www.mi5.gov.uk/careers/opportunities/digital-intelligence-operations
Investigations, Practices and Procedures: Seizure-Forensic Examination-Evidence. Cellular and Satellite Telephones, Call Records-Billing Data, Cell Site Analysis. Telecomms. Computer and Network Analysis. GPS devices & Jammers, Cyber, IoT forensics.
Wednesday, September 19, 2018
Saturday, July 07, 2018
Update - HERREVAD Databases Geo Location Artefacts
Back in February 2017 I wrote an article relevant to "HERREVAD Databases Geo Location Artefacts" (http://trewmte.blogspot.com/2017/02/herrevad-databases-geo-location.html) and I regularly conduct searches for any useful updates or supporting information that maybe of use.
-----
I see SANS DFIR in May 2018 published "Advanced Smartphone Forensics Poster - SANS Forensics" a poster to identify "Most Relevance Evidence Per Gigabyte" and includes the database 'Herrevad' (https://digital-forensics.sans.org/media/DFIR-Smartphone-Forensics-Poster.pdf).
-----
dmoreno1994's GeoAndroid .py script (https://github.com/NoSuitsSecurity/GeoAndroid)
positions an android phone without GPS by utilising the Herrevad database. "Herrevad: This database contains the WiFi connections history of preinstalled Google apps in Android OS devices. It can be WIFI connections of Google Play, Google Maps, Youtube, etc..
/data/com.google.android.gms/databases/herrevad"
-----
Posted yesterday 06/07/2018 Hybrid Analysis Incident Response malware analysis website (https://www.hybrid-analysis.com/sample/338a08badc67f40697db278e20390cf6dc2247e79e4b1845ea25e6c033c2572f?environmentId=200) illustrated Receiver and Intent involving Herrevad.
Receiver
com.google.android.gms.herrevad.receivers.CaptivePortalReceiver
Intent
android.net.conn.NETWORK_CONDITIONS_MEASURED
Receiver
com.google.android.gms.herrevad.receivers.GservicesReceiver
Intent
com.google.gservices.intent.action.GSERVICES_CHANGED
-----
An earlier version of Receiver and Intent is recorded in Joe Sandbox Cloud Analysis (https://www.joesandbox.com/analysis/39495/0/pdf) published 12 August 2017.
-----
Herrevad has an interest to those on Security Stack Exchange wanting to understand how the database can reveal SSID/Cell ID geolocation info. "How do you get Geolocation information from the CellID field in the herrevad database from Google Mobile Services? (https://security.stackexchange.com/questions/180971/how-do-you-get-geolocation-information-from-the-cellid-field-in-the-herrevad-dat)
-----
-----
I see SANS DFIR in May 2018 published "Advanced Smartphone Forensics Poster - SANS Forensics" a poster to identify "Most Relevance Evidence Per Gigabyte" and includes the database 'Herrevad' (https://digital-forensics.sans.org/media/DFIR-Smartphone-Forensics-Poster.pdf).
-----
dmoreno1994's GeoAndroid .py script (https://github.com/NoSuitsSecurity/GeoAndroid)
positions an android phone without GPS by utilising the Herrevad database. "Herrevad: This database contains the WiFi connections history of preinstalled Google apps in Android OS devices. It can be WIFI connections of Google Play, Google Maps, Youtube, etc..
/data/com.google.android.gms/databases/herrevad"
-----
Posted yesterday 06/07/2018 Hybrid Analysis Incident Response malware analysis website (https://www.hybrid-analysis.com/sample/338a08badc67f40697db278e20390cf6dc2247e79e4b1845ea25e6c033c2572f?environmentId=200) illustrated Receiver and Intent involving Herrevad.
Receiver
com.google.android.gms.herrevad.receivers.CaptivePortalReceiver
Intent
android.net.conn.NETWORK_CONDITIONS_MEASURED
Receiver
com.google.android.gms.herrevad.receivers.GservicesReceiver
Intent
com.google.gservices.intent.action.GSERVICES_CHANGED
-----
An earlier version of Receiver and Intent is recorded in Joe Sandbox Cloud Analysis (https://www.joesandbox.com/analysis/39495/0/pdf) published 12 August 2017.
-----
Herrevad has an interest to those on Security Stack Exchange wanting to understand how the database can reveal SSID/Cell ID geolocation info. "How do you get Geolocation information from the CellID field in the herrevad database from Google Mobile Services? (https://security.stackexchange.com/questions/180971/how-do-you-get-geolocation-information-from-the-cellid-field-in-the-herrevad-dat)
-----
Wednesday, February 14, 2018
Important principles in digital forensics
Schrodinger's Cat
https://upload.wikimedia.org/wikipedia/commons/thumb/9/91/Schrodingers_cat.svg/1200px-Schrodingers_cat.svg.png
At a time when digital forensics is under the spotlight and taking salvos of criticism for poor performance and lack of knowledge about its own scientific subject matter (http://parliamentlive.tv/Event/Index/7767e1b9-0e44-4de3-8627-baf9d091f487 and https://www.theguardian.com/uk-news/2018/feb/12/police-outsource-digital-forensic-work-to-unaccredited-labs) there is no better time than to refresh on principles to signpost the way to go or leave a breadcrumb trail to find the way back to safe ground.
I posted comments back in November 2006 (http://trewmte.blogspot.co.uk/2006/11/cell-site-analysis.html) identifying principles to remember, recall and apply, when conducting Cell Site Analysis (CSA) - but they apply to examinations also - that are still relevant to today (2G/3G/4G/5G/etc....) as they were since the inception of digital cellular radio services back in the late 1980s/1990s.
The requirements identified in standards as "mandatory", "conditional", "recommendations" and so on are not written for fun; nor to be wilfully disregarded just because they appear complex, complicated or difficult e.g. cannot be bothered to learn them, my device/machine does the thinking for me; both render the human-being to be no more than a perfunctory-goffer (human obsolescence) for the processes generated by software and algorithms in a device or machine.
The four principles to easily remember, recall and apply:
- There are mandatory requirements with mandatory outcomes
- There are mandatory requirements with optional outcomes
- There are optional requirements with mandatory outcomes
- There are optional requirements with optional outcomes
Moreover, and a fundamental (and one might suggest absolute) requirement, is the importance to understanding 'Modal verbs terminology' adopted in the standards.
Modal verbs terminology
In the present document "shall", "shall not", "should", "should not", "may", "may not", "need", "need not", "will", "will not", "can" and "cannot" are to be interpreted as described in clause 3.2 of the ETSI Drafting Rules (Verbal forms for the expression of provisions)
"must" and "must not" are NOT allowed in ETSI deliverables except when used in direct citation.
Wednesday, January 10, 2018
URN Namespace and IMEI
RFC8141 - A Uniform Resource Name (URN) is a Uniform Resource Identifier (URI) [ RFC3986] that is assigned under the "urn" URI scheme and a particular URN namespace, with the intent that the URN will be a persistent, location-independent resource identifier. A URN namespace is a collection of such URNs, each of which is (1) unique, (2) assigned in a consistent and managed way, and (3) assigned according to a common definition. (https://tools.ietf.org/pdf/rfc8141.pdf).
RFC7255 - This specification defines how the Uniform Resource Name (URN) reserved for the Global System for Mobile Communications Association (GSMA) identities and its sub-namespace for the International Mobile station Equipment Identity (IMEI) can be used as an instance-id. Its purpose is to fulfil the requirements for defining how a specific URN needs to be constructed and used in the ’+sip.instance’ Contact header field parameter for outbound behaviour. (https://www.rfc-editor.org/rfc/pdfrfc/rfc7255.txt.pdf).
RFC7254 - This specification defines a Uniform Resource Name (URN) namespace for the Global System for Mobile Communications Association (GSMA) and a Namespace Specific String (NSS) for the International Mobile station Equipment Identity (IMEI), as well as an associated parameter for the International Mobile station Equipment Identity and Software Version number (IMEISV) as per the namespace registration requirement found in RFC 3406 [ 1]. The Namespace Identifier (NID) ’gsma’ is for identities used in GSM, Universal Mobile Telecommunications System (UMTS), and Long Term Evolution (LTE) networks. The IMEI and the IMEISV are managed by the GSMA, so this NID is managed by the GSMA. (https://tools.ietf.org/pdf/rfc7254.pdf).
Image courtesy of Diameter-Protocol
RFC7255 - This specification defines how the Uniform Resource Name (URN) reserved for the Global System for Mobile Communications Association (GSMA) identities and its sub-namespace for the International Mobile station Equipment Identity (IMEI) can be used as an instance-id. Its purpose is to fulfil the requirements for defining how a specific URN needs to be constructed and used in the ’+sip.instance’ Contact header field parameter for outbound behaviour. (https://www.rfc-editor.org/rfc/pdfrfc/rfc7255.txt.pdf).
RFC7254 - This specification defines a Uniform Resource Name (URN) namespace for the Global System for Mobile Communications Association (GSMA) and a Namespace Specific String (NSS) for the International Mobile station Equipment Identity (IMEI), as well as an associated parameter for the International Mobile station Equipment Identity and Software Version number (IMEISV) as per the namespace registration requirement found in RFC 3406 [ 1]. The Namespace Identifier (NID) ’gsma’ is for identities used in GSM, Universal Mobile Telecommunications System (UMTS), and Long Term Evolution (LTE) networks. The IMEI and the IMEISV are managed by the GSMA, so this NID is managed by the GSMA. (https://tools.ietf.org/pdf/rfc7254.pdf).
Tuesday, November 07, 2017
100 Years - Remembrance Day 11/11/2017
I do not know the artist but the message in the painting below is understood. If you haven't done so and you see a person selling Poppies do stop and buy one; even if you give 5p it goes to a good cause.
We stand on the shoulders of those who fought and gave us "freedom and liberties" which are so easily taken for granted today.
REMEMBRANCE DAY
11th NOVEMBER (1917-2017)
We stand on the shoulders of those who fought and gave us "freedom and liberties" which are so easily taken for granted today.
Sunday, October 29, 2017
Understanding Metadata
NISA 2017 - UNDERSTANDING METADATA - WHAT IS METADATA, AND WHAT IS IT FOR? is available. Surprisingly, not read anywhere else that this update was out, being that it is a highly relevant subject to digital (mobile, computer, audio, etc.) forensics.
http://www.niso.org/apps/group_public/download.php/17446/Understanding%20Metadata.pdf
Android CDD
As of the 1st September 2017 Android published their updated Compatibility Definitions Document version 8.
9.8.1 . Usage History - Android stores the history of the user's choices and manages such history by UsageStatsManager . Device implementations: [C-1 -1 ] MUST keep a reasonable retention period of such user history. [SR] Are STRONGLY RECOMMENDED to keep the 1 4 days retention period as configured by default in the AOSP implementation.
See also: 9.9. Data Storage Encryption, 9.9.2. File Based Encryption, 9.9.3. Full Disk Encryption,
https://source.android.com/compatibility/android-cdd.pdf
Face Recognition
Following Apple's Face ID launch this is one of those hot topics at the moment. This technology is not without its sceptics and questions still remain whether it can become full proof. In today's world, that is a big ask.
I have collected some bits and pieces worth reading.
Apple's September 2017 paper on face ID and security - [https://images.apple.com/business/docs/FaceID_Security_Guide.pdf]
Kairos produce a useful comparison chart of facial recognition services[https://www.kairos.com/blog/face-recognition-kairos-vs-microsoft-vs-google-vs-amazon-vs-opencv]
The Guardian Newspaper published an article of Samsung's flawed Iris scanner - [https://www.theguardian.com/technology/2017/may/23/samsung-galaxy-s8-iris-scanner-german-hackers-biometric-security]
New research proposal just out 'Bypassing 3D Facial Recognition Authentication on Mobile Devices' - [https://www.os3.nl/_media/2017-2018/courses/ssn/projects/ssn_proposal_01.pdf]
NCSC Cyber Security: Small Business Guide
Cyber security can feel like a daunting challenge for many small business owners. But it needn’t be. Following the five quick and easy steps outlined in this guide could save time, money and even your business’ reputation.
Threema - white paper
Latest white paper Sept 2017
https://threema.ch/press-files/2_documentation/cryptography_whitepaper.pdf
Threema-iTunes
Threema is the world’s favourite secure messenger and keeps your data out of the hands of hackers, corporations and governments. Threema can be used completely anonymously, allows to make end-to-end encrypted voice calls, and offers every feature one would expect from a state-of-the-art instant messenger.
Useful for running lab tests.
https://itunes.apple.com/gb/app/threema/id578665578?mt=8
Useful for running lab tests.
https://itunes.apple.com/gb/app/threema/id578665578?mt=8
Childrens' Smart Watch Tracking Movements
Is a stranger hacking your child's smart watch? Warning that loopholes in the devices are being targeted to track youngsters' movements.
Daily Mail Science Tech Article 4991102
Very Low Cost Training $99.00 - US Marketplace
Just been reading a post from Dennis Carroll Special Agent / Law Enforcement Instructor about some very low cost training in the States
"The Fox Valley Technical College in partnership with the National Criminal Justice Training Center (NCJTC) have approved my three day cellular device investigations course. The first course is being offered in Appleton Wisconsin in December as a pilot and then throughout the US as requested. The FVTC and NCJTC have obtained a grant to lower the cost of this course to $99. This is the lowest price you will find for a three day comprehensive cellular device investigation course. There is a link to request this course at your host agency on the link below. Please share if you would."
https://ncjtc.fvtc.edu/training/details/TR00005533/TRI0005534/cellular-device-investigations
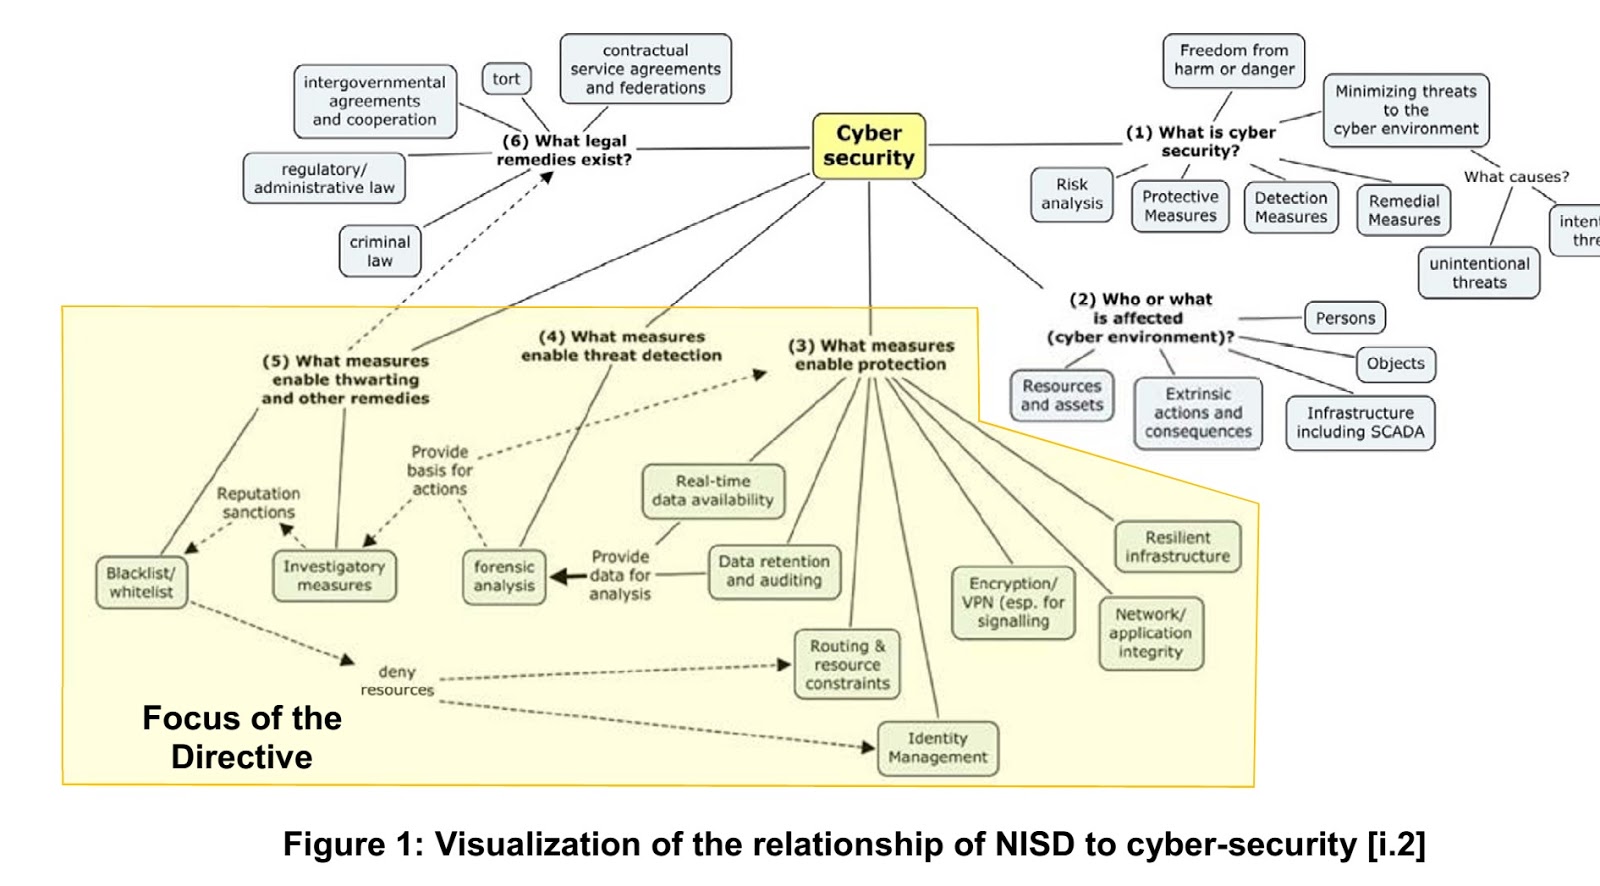
New Cyber Report recognises legal actions
June 2015 I sketched foreseen legal actions impacting on cybercrime. I posted a diagram-infographic in Feb 2016 "LEGALLY SPEAKING – OBSERVATIONS CHART FOR JUDGES BARRISTERS AND SOLICIT0RS" - http://trewmte.blogspot.co.uk/2016/02/threatware-legally-speaking.html.
I am pleased to see that ETSI (European Telecommunications Standards Institute) have also picked up on my themes in their 2017 published technical report (TR) CYBER; Implementation of the Network and Information Security (NIS) Directive ETSI TR 103 456 V1.1.1 (2017-10) with reference to Contract, Tort and Crime.
Labels:
actus reus,
barristers,
case law,
civil law,
crime attacks,
criminal law,
cybercrime,
ETSI,
intention,
Judges,
malware,
mens rea,
mistake,
solicitors,
TC Cyber,
Threatware
Sunday, October 08, 2017
Sunday, September 10, 2017
Dolphin Ultrasonic Commands Voice Assistance
Photo source: https://upload.wikimedia.org/wikipedia/commons/thumb/b/b3/Dolphind.jpg/200px-Dolphind.jpg
A newly issued report makes me wonder whether a Dog Whistle could issue commands to voice assistance devices? Dolphin ultrasonic audio, not within human hearing range, can issue commands to voice assistance Amazon, Apple and Google devices according to a news report from the BBC - http://www.bbc.co.uk/news/technology-41188557.
The basis of the BBC report is underpinned from Chinese research that can be found here: Dolphin Attack: Inaudible Voice Commands - https://endchan.xyz/.media/50cf379143925a3926298f881d3c19ab-applicationpdf.pdf.
Tuesday, August 22, 2017
Universal Network Investigations Updates
Universal Network Investigations (at LinkedIn) is a discussion group exists to assist telecoms, cyber, forensics, information security, pen testing, and fault-finding investigations: to exchange observations and sharing 'intel' in a closed forum discussing fixed and mobile network investigations - trace data and other forms of evidence (including but not limited to PCAP, CDRs, traffic logs, exchange and switch data, cell details, dumps, etc.). Investigations can start with examining a device or network activity, so all aspects will be posted in the group.
To join - https://www.linkedin.com/groups/13536130
Group Rules:
1) Chatham House Rule applies.
2) An essential aspect of joining the Group is to participate and share knowledge, skills and experience.
3) No selling, no spamming.
Latest Posts
- Dropped phones
- Tool for the Investigator ISMS Toolbox
- Apple Secure Enclave Processer (SEP) - Hacked
- Purging Data HDD (InfoSec)
- Rack and Ruin
- When a Genuine Product is used as a Rogue Device
- GDPR
- GDPR-1
- Framework for Digital Forensic Employment KSE (knowledge, skills, experience)
- VOIP Basics (updated)
- Tool for the Investigator ISMS Toolbox
- BGP
- Cisco IOS Versions
- EIGRP
- First Hop Redundancy
- Frame Mode MPLS
- IEEE 802.11 WLAN
- IOS Interior Routing Protocols
- IOS IPv4 Access Lists
- IOS Zone Based Firewall
- IPSec
- IPv4 Multicast
- IPv6
- IS-IS
- NAT
- OSPF
- Physical Terminations
- PPP
- QoS
- RIP
- Scapy
- Spanning Tree
- TCP Dump
- VLANs
- Wireshark Display Filters
- BILL - Internet of Things IoT Cybersecurity Improvement Act
- 1995-2017 Computer Security (Information Security)
- So what does the TIMSI get me?
- Federal data collection MRMCD
- Tech Against Terrorism
- Telecommunications (Interception and Access) Act 1979 (2017) (Australia)
- 27,482 cyber security incidents reported in H1 2017
- Surveillance Drones Report
- Smartphone Cybercrime
- PSCR Network Identifiers Demonstration Guidelines
- Plan MNC
- Ping Test
- MNC Probe Metrics
- ITU-T GSM Country Codes
- IMSI Prepaid MVNO
- G42UMTS Security
- Cyber Threats to Mobile Phones
- Building Mobile Tools for Rights Defenders and Activists
- USER INVASION TESTS ON SAMSUNG GALAXY J3-6 J320FN
- UTC Document Register
- IMSI Assignment and Management Guidelines and Procedures
- Evolution in the Use of E.212 Mobile Network Codes
- 3rd Party Access to Number Portability Data
- Evolution in CLI usage
- Wrong Evidence Capture Tools
- Phone Hacks
- Multi-Traceroute (MTR) in NST
- NST
- Detecting Hidden Networks created with USB Devices
- Infrastructure - human access - fake fingerprint
- Operator 'Law Enforcement Disclosure' reporting
- Covert Tactical Measures
- NUMBERING PLAN ASSISTS TRACE
- Annual Cybersecurity Report - 2017
- Infrastructure Security Report - Worldwide
- Real Intelligence Threat Analysis (RITA)
- GSM Security Threat Risks
- Where to begin?
- RSOE EDIS Emergency and Disaster Information Service
- GSM Security Threat Risks
- NOC NOC - Fault Management and Troubleshooting
- SS7 and 2FA
- Detection in a multilayer network
- Diameter - Online Charging Systems (OCS)
- Big / Fresh / Deep - Data : Huaewi overview
- Hot technologies to know about
- ARP.pcap
- bgp.pcap
- https.pcap
- ICMP-ARP-OpenFlow1.0.pcap
- ICMP-DHCP-DNS.pcap
- Russians target Telegram App
- Wireshark
- Protocols Relevant to U-N-I
- Industrial Networks Hit By WannaCry
- IM Telegram Replay Attack - Android
- Whisper Signal WhatsApp
- Subpico Intelligent Application Layer Software
- Subpico LI with evidential integrity
- TraceWrangler
- old_GUTI_IMSI_Critical_Reject (updated)
Saturday, August 12, 2017
Field Project Investigations
Conducting a technology review/audit prior to commencing field projects is an important task in order to understand the 'technology estate' owned and/or operated by an organisation. It is for revelation purposes and to comprehend [legacy] technology as stand-alone or interconnected/intra-connected with [current] technology and significantly if or how legacy has been ported-over to operate via applications/software to work with current. So more information has been posted. This is for the purposes as mentioned previously dealing with cases requiring 'field project investigations' (from installs to troubleshooting). I am sharing these .pdfs because I found forensics became one of the tools to be applied during investigations and not the main tool. Knowing the background details (tech spec, set-up, logs files, install procedures, etc.) assists understand "why an artefact was there".
To read the posts - https://www.linkedin.com/groups/2436720
Latest Updates: Institute for Digital Forensics
- Windows Registry Reference
- Apple Reference Cards and iPad iOS7 Quick Guide
- USB Guide & USB Key Guide
- Hardware Configuration Dell Precision WorkStation
- Legacy DOS
- 100 Windows 8 Keyboard Shortcuts
- 100 Chrome Tips
Institute for Digital Forensics - Previous Updates
- Tron Commands
- Malware, Junkware, Virus
- Checking Implemented Security
- Backups
- Troubleshooting, Tips and Guides
- Windows NT Server Resource Reference
- Admin Tools To Know and Explained
- Corrupted Registry
- Windows Resource Kit Reference
- Fasteners
- Projects - Win 10
- Projects - Win 8
- Projects - Win 7
- Vulnerabilities in Critical Evidence Collection
- Imaging with Image-X: The Ghost Killer
- A Guide for the Forensically Sound Examination of a Macintosh Computer
- Interpol's Forensic Report on FARC Computers and Hardware
- Reducing Data Lifetime Through Secure De-allocation
- Realising - Risk Sensitive Evidence Collection
- Notes on Computer Systems and Operating Systems
- Finding Child Porn in the Workplace
- Drafting Electronic Evidence Protocols
- Data Hiding in Journaling File Systems
- Investigation of Protected Electronic Information
- Electronic Evidence: The Ten Commandments
- Electronic Evidence Best Practices
- Laws of evidence in criminal proceedings throughout the European Union
- Evaluating Commercial Counter-Forensic Software
- Hacking into computer systems
- Windows device interface security
- NSA Redacting with Confidence: How to Safely Publish Sanitized Reports
- Reproducibility of Digital Evidence
- Windows Memory Analysis
- Secure Deletion Myths
- Spoliation of Evidence
- Forensic Discovery
- VMware to boot cloned/mounted hard disk images
- Volume Serial Numbers: Format Verification Date/Time
Subscribe to:
Posts (Atom)