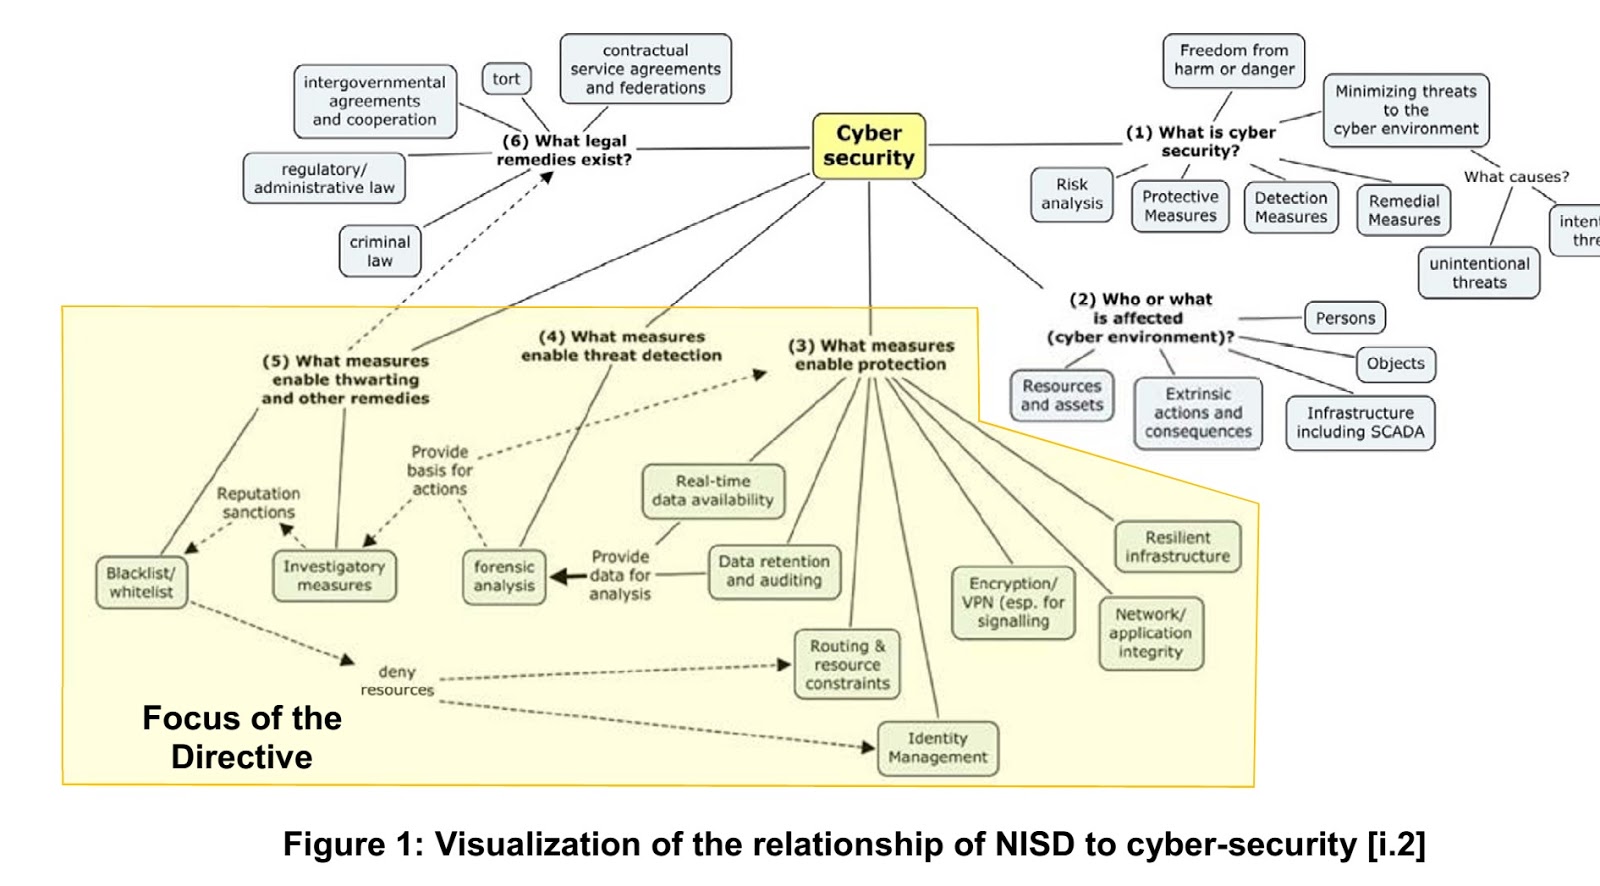
LEGALLY SPEAKING – OBSERVATIONS CHART
FOR JUDGES BARRISTERS AND SOLICIT0RS
The courts maybe faced with dealing with a wide range of mobile and computer criminal cases and civil disputes. These may include exploitation of the latter devices. Given the explosion of discontent in the world the use of "threatware" (a vernacular term adopted for this discussion) requires identification as to the type of threat defined by the outcome.
SKILLED OPINION
The supposed threat may not be enough by simply labelling it a threat - a victim's experience may not amount to a skilled opinion: The
evidence was held not to be admissible on the grounds inter alia that no expert had given evidence as to the records, and
that any connection they displayed between the cars stolen and those connected
with the accused was a question of fact, not as in Abadom a question of
opinion - Myers .v. D.P.P. [1965] A.C. 1001.
LABELLING THREATWARE
Calling a program "threatware" may require more than a simple label being attached to it; proof that it is what it is claimed to be a court may require substantiation: Patel v Controller of Customs [1966] AC356 held the words “produce of Morocco” stamped upon bags of
coriander were inadmissible to prove the country of origin of the coriander. The words were stamped on the bag with
express intention of asserting a fact and were thus hearsay.
STORAGE MEDIA
A person having threatware may amount to possession but not intention to use. Equally, the definition of storage container vis-à-vis stored computer may also be subject to definition of 'computer' in e.g. civil law: Section
5 ss6 Civil Evidence Act 1968 - (6) Subject to subsection (3) above, in this Part of this Act " computer " means any device for storing and processing information, and any reference to information being derived from other information is a reference to its being derived therefrom by calculation, comparison or any other process. Also see Civil Evidence Act 1972 and 1995 for hearsay and opinion.
CONTRACTUAL DISPUTE
Where threatware is involved in the form of ransomware that arises in contractual dispute between parties see - Ordanduu GmbH & Anor, R (On the Application Of) v Phonepayplus Ltd [2015] EWHC 50 (Admin) (16 January 2015)
DATA PROTECTION
For a case where ransomware and data protection are involved see - CASE STUDIES 2013 - Data Protection Commissioner - Ireland [2013] IEDPC 18 (2013)
MALWARE AS THREATWARE
Cyber Warfare: A Review of Theories, Law, Policies, Actual Incidents – and the Dilemma of Anonymity | Reich | European Journal of Law and Technology:
Speaking of the problem of attributing, General Alexander notes that it is very hard "telling one actor from another and divining actors' intentions":
Not every event that affects our networks rises to the level of a national security threat. It is important to remember that hacking, spreading malware and other malicious activities are crimes, defined domestically as well as internationally by the Convention on Cybercrime, and accordingly have legal consequences. Even if you spot an intrusion and you know it originated from an adversary, you usually cannot tell an intelligence operation from a military one. (*page 5)
As part of the overall strategic plan of the US Department of Defense, emphasis must be placed on deterrence. General Alexander notes:
Attacks by hackers and criminals can cause "nation-state sized" effects; indeed, the accidental "release" of malware might do the same, and the problem of attributing the attack to a particular actor similarly remains difficult to impossible. We have to study deterrence anew, from a variety of perspectives, and to gain clarity on our authorities. To take a thought from Sun Tzu, we must understand the cyber environment and, the capabilities of our adversaries, and our own abilities as well. This is not going to be easy, and it is not going to yield answers soon. If we know one thing from the Cold War, it is that stable deterrence can take years to achieve, and is the product of planning, analysis, and dialogue across the government, academe, and industry, and with other nations as well. Cyber deterrence will require progress in situational awareness, defense, and offensive capabilities that adversaries know we will use if we deem necessary. (*page 5)
The above is a small sample of what is available regarding title variations, possible definitions and legal classification that may have bearing when dealing with threatware. I am not a lawyer merely I am simply using legal references to help support points in this discussion and suggesting a possible direction to seek further clarifications, observations or advice.